This manual is for HRM FPX 5401 Assessment 3, start to submission. Legal and Ethical Considerations in Healthcare Privacy: Brief asks you to brief leaders on patient privacy: how HIPAA affects the regulatory environment and the industry, the legal and ethical basis for privacy, how compliance supports quality care, the issues raised by electronic storage of and access to records, and best practices HR can use to prevent violations. The grade turns on practical, accurate guidance. A brief that connects the rules to staff behavior and HR controls scores above a summary of the law. Below is the method our tutors use, a structure that maps to the criteria, and an annotated sample excerpt. Prefer to hand it off? A premium original sample for this exact assessment comes back in 24 to 48 hours, revised free until it meets the guide. Capella's catalog lists the course as HRM-FPX5401, and some courserooms print HRM5401; both point to this same Assessment 3. In current courserooms this assessment typically appears as "Legal and Ethical Considerations in Healthcare Privacy: Brief".
One honesty note before the manual: Capella revises courses and scoring guides over time, so always write to the exact scoring guide attached to your assessment in the courseroom. The course identity above is verified on capella.edu; the method and structure below are our tutors' approach to it, not Capella's official rubric text.
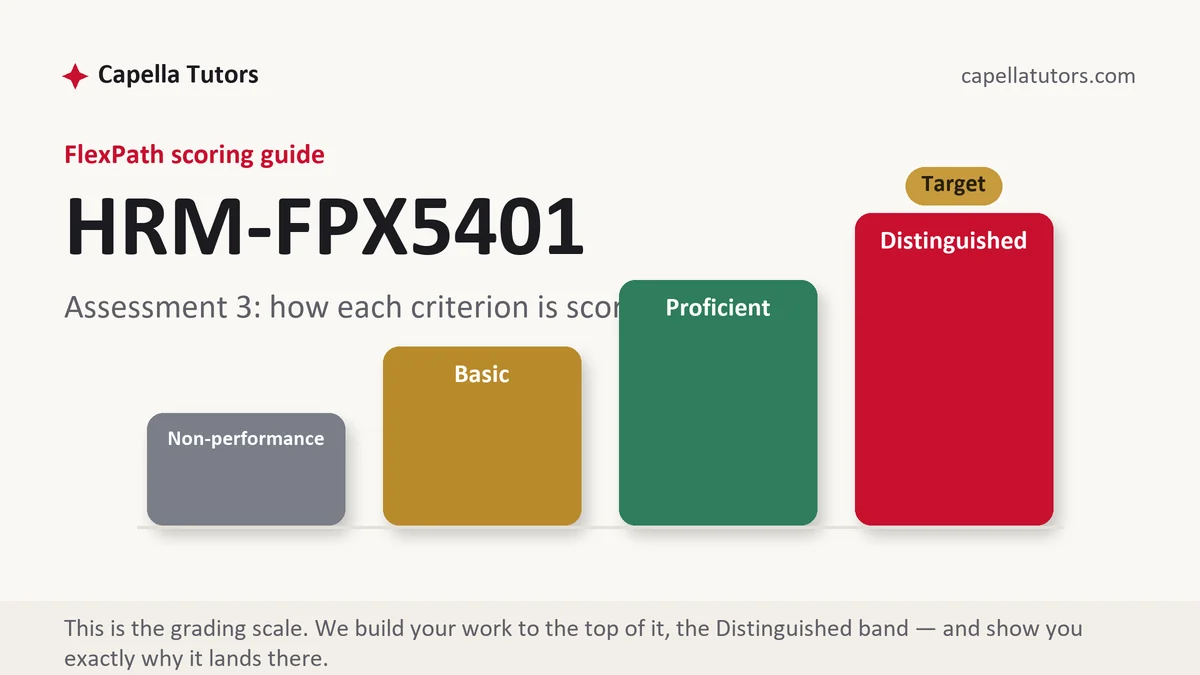
How HRM FPX 5401 Assessment 3 is scored
FlexPath does not use letter grades. Each criterion in the scoring guide lands on one of four levels, and the level descriptions are the real writing brief:
| Level | What it means on a privacy brief |
|---|---|
| Distinguished | The privacy brief is specific to the organization or case, applies course concepts accurately with credible sources, and ends in justified conclusions or recommendations. |
| Proficient | The privacy brief is accurate, but the application or recommendations are general. |
| Basic | The privacy brief describes concepts with little application. |
| Non-performance | A required part of the privacy brief is missing. |
Cite the HIPAA Privacy and Security Rules accurately.
The HRM FPX 5401 Assessment 3 method, step by step
-
Explain HIPAA's impact
Privacy, Security and Breach Notification Rules.
-
State the legal and ethical basis
Law, professional ethics and trust.
-
Link compliance to quality
Why privacy supports care.
-
Address electronic records
Access controls, audit logs, minimum necessary.
-
Recommend best practices
Training, monitoring and sanctions.
-
Define HR's role
Policies, training and discipline.
A structure that maps to the criteria
Word counts are planning targets our tutors use, not Capella rules; follow the length and format your scoring guide states.
| Section | What it must do | Guide |
|---|---|---|
| Introduction | Purpose. | ~75 words |
| HIPAA impacts | Rules explained. | ~200 words |
| Legal and ethical basis and quality | Analysis. | ~200 words |
| Electronic records and best practices | Guidance. | ~250 words |
| References | Sources. | as needed |
Annotated sample excerpt
An original model excerpt from our team, written to show the register that reaches the top of the guide. Learn the moves, then write your own version.
The most common privacy violations involve staff looking at records they have no work reason to see, such as a coworker's or a local celebrity's chart.1 Audit logs make that visible, and regular audits combined with a clear sanctions policy, applied consistently, deter it far more effectively than annual training alone.2 HR's part is to make the policy known at hire, to enforce it the same way for everyone, and to document each case, since inconsistent discipline creates its own legal risk.3
- 1Identifies the most common violation.
- 2Recommends controls that work.
- 3Defines HR's role precisely.
The full premium sample for your exact assessment, written fresh to your scoring guide and topic, is free to request. Study it, revise it into your own voice, and submit work you understand.
The five mistakes that cost Distinguished
- Definitions without application. Apply each concept to the organization or case.
- No sources. Cite credible business sources.
- Vague recommendations. Make them specific and justified.
- Law without practice. Turn rules into controls.
Pre-submission checklist
- HIPAA impacts
- Legal and ethical basis
- Quality link
- Electronic records
- Best practices
- HR role and references
Want the privacy brief written?
Send the scoring guide and any materials from your courseroom. Our team returns a premium original privacy brief in 24 to 48 hours, revised free until it meets the guide.